Bangladesh Bank Website Restored After 3-Day PHP Cyberattack Shutdown
Central bank took the site offline as a precaution while internet and mobile banking continued without disruption
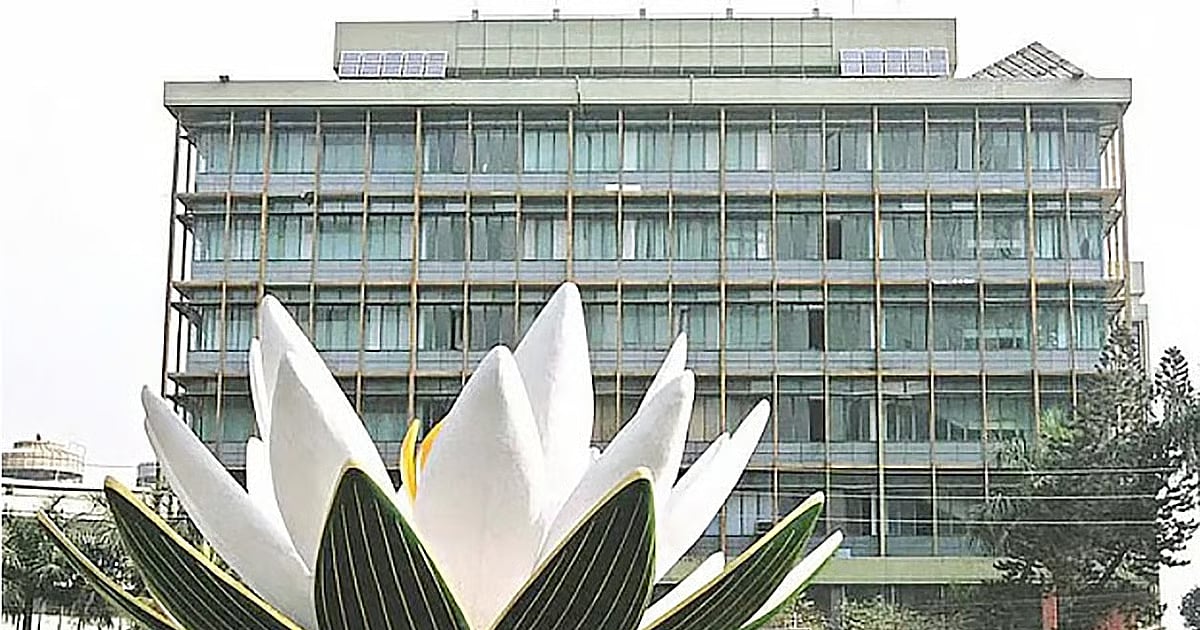
✅ Bangladesh Bank's official website, taken offline last Thursday amid fears of a cyberattack, was restored at 8:00am on Sunday after three days — closing out the country's highest-profile precautionary shutdown during last week's global PHP vulnerability scare. Crucially for the financial system, internet banking and mobile banking transactions continued as normal throughout the three days, so customers faced no disruption to their payments.
📞 Bangladesh Bank spokesperson Arif Hossain Khan told Prothom Alo on Sunday that the website had been checked for possible vulnerabilities before being brought back. The decision to take it offline was made amid fears of attacks worldwide, and as the risk has subsided, the website has been restored, he said — a measured account of a deliberately unglamorous operation: patch first, verify, then reopen.
🌐 The context is the global scare that unfolded around two serious security vulnerabilities discovered in PHP, the programming language that powers a large share of the world's websites — including many operating government services, banking platforms, e-commerce sites and news outlets in Bangladesh. According to reports by the BBC and Reuters, governments in various countries took emergency measures after the vulnerabilities were identified, and from Wednesday night, governments and commercial organisations around the world began shutting down their websites. Despite those precautions, reports in various media outlets indicate that millions of hacking attempts were made against exposed systems.
🛡 What the episode actually tested
🏦 For Bangladesh Bank, the shutdown was an unusual public admission that a central bank's own web estate sits on the same vulnerable software as everyone else — and that taking the public face of the institution offline for three days was judged safer than leaving it exposed. The restoration sequence, with transactions unaffected throughout, also quietly demonstrated something regulators have preached for years: that the website and the transaction rail are different assets. A defaced or exploited portal embarrasses an institution; a compromised payment switch is a systemic event. Keeping the two decoupled is exactly what allowed the precaution to be taken without financial cost.
💻 The wider lesson for Bangladeshi institutions is procedural rather than technical. The institutions that weathered the week best were those that could answer three questions quickly: exactly which systems run which software, which of those are internet-facing, and how fast can each be patched or isolated. Bangladesh Bank's three-day closure suggests its inventory answered all three — while the central bank's earlier alert through BGD e-GOV CIRT pushed every other government agency, bank and telco to answer the same questions for themselves. Where answers were slow, this week exposed the gap loudly.
⚡ The restoration also carries a caution: PHP2Shell-style vulnerabilities are typically followed by waves of copycat research, with security researchers — and attackers — using AI-assisted scanning to find neighbouring flaws in the same codebases. A website restored today is not a website secured forever; the patch calendar, the vulnerability scans and the incident-response drills that the last week made mandatory are now the permanent operating cost of being online.
🔭 For the financial sector specifically, the smooth outcome should not breed complacency but confidence in process: the central bank treated a global alert as a domestic incident, acted visibly, and reopened with an all-clear message. That template — rapid triage, transparent communication, uninterrupted core services — is one the sector's commercial banks, bKash-style fintechs and digital government platforms will do well to institutionalise before the next global vulnerability drops without warning. The internet ran out of warnings to give; the next test will arrive exactly as this one did, in a disclosure feed rather than a weather forecast.
📄 The disclosure timeline deserves one more note. The vulnerabilities were publicly detailed in the middle of last week; within hours, Cloudflare and other monitoring firms reported millions of exploit attempts worldwide; within a day, governments from Tokyo to Helsinki had shuttered services. Bangladesh's institutions — from the central bank to commercial lenders such as Janata Bank and Bengal Commercial Bank, which took their own sites down amid the same fears — were operating on a response clock measured in hours, not weeks. That is a demanding tempo for any domestic IT department, and it is now the permanent tempo of global cybersecurity: every institution in Bangladesh that depends on foreign-developed software inherits every future flaw in that software the moment it is disclosed.
🚀 There is a positive precedent to bank here as well. The country's digital financial infrastructure — the interbank switches, mobile financial services and payment gateways that processed normally through three days of elevated alert — passed a live stress test without visible incident. For an economy that has moved hundreds of millions of daily transactions onto rails built in the last decade, uninterrupted service during a global scare is not a small achievement; it is evidence that the sector's redundancy, monitoring and separation-of-duties investments have substance behind them. The task now is extending that same resilience discipline to the public-facing web estate, where this week showed the country remains most exposed.
This news was originally published by Prothom Alo English. For the full original report, please visit: https://en.prothomalo.com/business/local/stvlg9as79
📬 Get Bangladesh Trade News in your inbox
Weekly digest of export industry news, policy updates, and market analysis.
📰 Related Stories